
Two MIT researchers have shown that precisely timed interrupts can get past the Spectre v2 defenses in recent Intel and AMD processors, and they built a working exploit that leaked Linux password hashes from an AMD Zen 2 machine.
Daniël Trujillo, a PhD student, and associate professor Mengjia Yan of MIT’s Computer Science and Artificial Intelligence Laboratory (CSAIL) call the attack class TONTOU, for Time-of-Neutralization to Time-of-Use. They presented it at Black Hat USA, and BleepingComputer reported they will also present it at USENIX Security 2026, Oct. 27 to 29.
The gap after the wipe
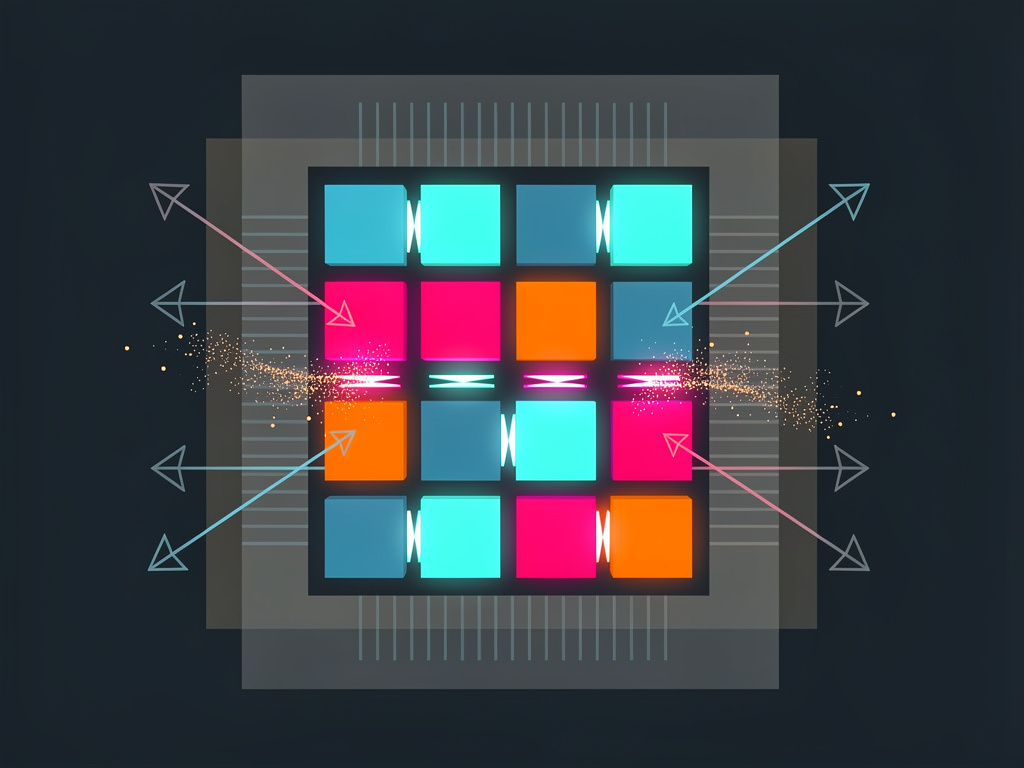
Many Spectre v2 mitigations neutralize branch predictor state before sensitive code runs. Intel’s eIBRS sanitizes branch predictors on a context switch, and AMD’s Safe RET, introduced after the 2023 Inception attack that Trujillo co-authored, cleans state immediately before a protected branch executes, The Register explained. Both assume nothing can tamper with the predictor between the cleaning and its use.
“There is always a gap — sometimes only a handful of instructions wide. Anything that runs in that gap can dirty the machinery all over again,” MIT CSAIL wrote in its account of the work.
The researchers’ technique, which they call interrupt injection, has an unprivileged program schedule high-frequency timer interrupts so that one lands inside that window. The interrupt handler then re-poisons structures such as the return stack buffer or branch history buffer, so a protected branch speculatively jumps to a gadget that leaks kernel data through a side channel. On AMD, Safe RET leaves a window just two instructions wide, and the team hit it by slowing the processor down at that spot, according to CSAIL.
They saw mispredictions on Intel Cascade Lake Refresh and Arrow Lake processors and on AMD Zen 2 and Zen 4 chips. They built a full end-to-end exploit only for Zen 2, The Register reported, largely because the Intel attack requires specific software conditions.
What the exploit got
On a Zen 2 system running Linux 6.14 with default mitigations, the attack broke kernel address space layout randomization in all ten tries, in about nine minutes each, per CSAIL. It then read kernel memory at 5.47 bytes per second with 91.97% accuracy and extracted the Linux shadow password file, which holds the root password hash, in five of the ten runs, with each attempt averaging 18 minutes, BleepingComputer reported.
“It’s definitely not a simple attack, but we show that it’s practical with our end-to-end exploit on AMD Zen 2,” Trujillo told The Register. “Any time you’d execute unprivileged code with timer availability on a system while sharing the kernel with a victim, this attack would be an issue.” He gave multi-tenant container platforms as an example.
Vendor responses
AMD’s bulletin AMD-SB-7061 credits Trujillo and says the behavior was demonstrated on Zen 1 and Zen 2, with Zen 3 and Zen 4 possibly affected but not demonstrated. AMD said the issue “appears to be associated with the Linux implementation of the Safe RET mitigation.” According to CSAIL, AMD released a patch that users get by updating their operating system.
Intel told the researchers it won’t develop other mitigations because real-world exploits depend on too many factors, such as the availability of disclosure gadgets, though it paid a bug bounty in the hundreds of dollars, The Register reported. Arm said the technique falls under “passive leakage,” which it does not “actively protect against.”
The paper suggests cleaning the predictor a second time when the interrupt finishes. That looks workable on AMD, but on Intel it could make the attack more reliable, CSAIL said, while newer Intel chips include a dedicated instruction that appears to help. The researchers notified AMD and Intel in early February and Linux kernel maintainers in March, and their paper and code are public.


 WebProNews is an iEntry Publication