
Microsoft released fixes for 1,093 security flaws on Tuesday, its second straight monthly update above 1,000. Only one was already under attack, an Outlook bug that hands attackers a user’s NTLMv2 password hash, and Microsoft’s advisory credits its discovery in part to a researcher working with Anthropic’s Claude.
The size of these releases has changed fast. A year ago, Microsoft’s November release carried 63 new CVEs assigned by the company, according to its own update data; this one carried more than 17 times as many. Researchers tie the jump to AI-assisted bug hunting. Tenable’s Satnam Narang told CSO Online that “for most of the year, AI has been building bigger haystacks across Patch Tuesday releases, and this appears to be the first time it has found a needle.”
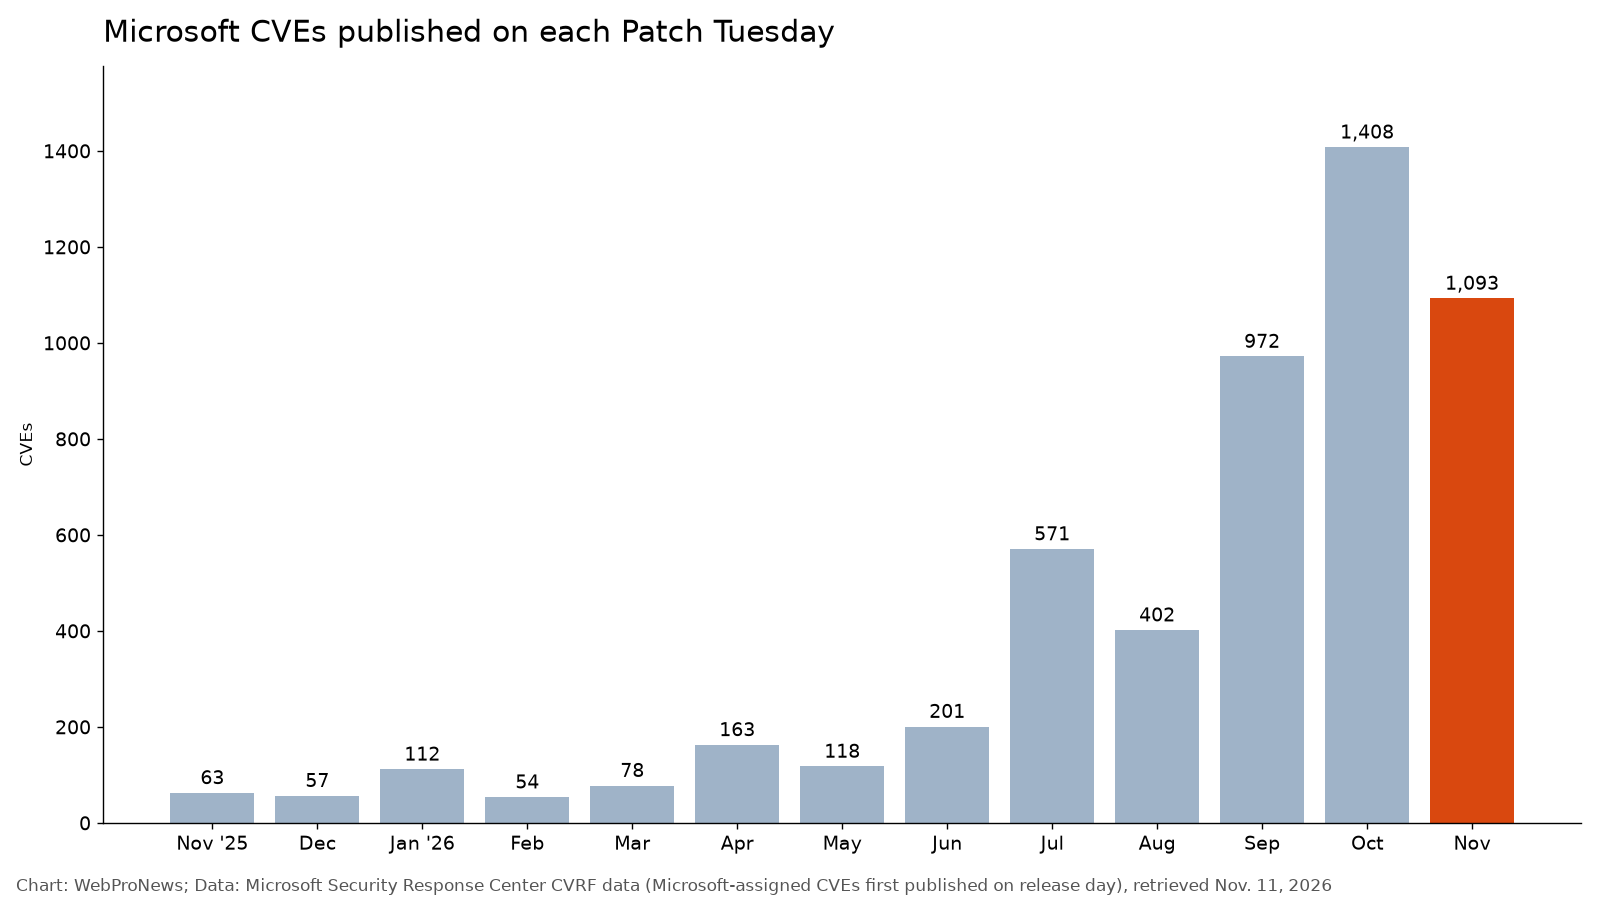
The count peaked in October, when Microsoft published more than 1,400 CVEs in a single day, a release WebProNews covered at the time. November’s batch includes 63 critical, 1,029 important and one moderate-rated flaw, Tenable’s breakdown shows. Elevation-of-privilege bugs make up 48.9% of the total and remote code execution 27.1%.
The exploited flaw, CVE-2026-124194, is the one moderate. It carries a CVSS score of 6.5 and is labeled spoofing. An attacker sends a crafted message file and persuades the target to open it. Outlook then connects to an attacker-controlled network location “without displaying the usual external-content warning,” Microsoft said, and gives up the user’s NTLMv2 hash. The attacker “could use this to authenticate as the user.” The Preview Pane is not an attack vector. Fixes cover Microsoft 365 Apps for Enterprise and Office LTSC 2021 and 2024. Microsoft hasn’t said who is using the bug or against whom.
Dustin Childs, head of threat awareness at the Zero Day Initiative, wrote in his monthly review that “the impact is bigger than the name suggests” and told readers not to let the low score lull them. The Cybersecurity and Infrastructure Security Agency added the flaw to its Known Exploited Vulnerabilities catalog the same day and gave federal civilian agencies until Nov. 24 to patch.
Microsoft’s acknowledgment lists “Benoît Sevens using Claude with Anthropic” alongside a researcher who goes by nono. Tenable noted that the advisory doesn’t name a Claude version. WebProNews has reported on how AI is helping attackers work faster against fresh patches, and Childs made a related point: seeing fewer zero-days exploited in the wild “makes sense, as AI is better at reversing patches than it is at finding and exploiting bugs in closed-source software.”
That makes the unexploited bugs the bigger scheduling problem. Two critical remote code execution flaws score 9.8 and need no user interaction: one in Windows Search (CVE-2026-116928) and one in Windows LDAP (CVE-2026-119958), both out-of-bounds writes that Microsoft says let an unauthorized attacker execute code over a network. Microsoft rates both “exploitation less likely.” It rates a critical Exchange Server bug (CVE-2026-118207) and an Active Directory Domain Services flaw (CVE-2026-118146), each scored 8.8, as “exploitation more likely.” Childs counts 30 CVEs this month that he considers wormable, and his advice to The Register was to “patch Exchange and Domain Controllers (LDAP/Kerberos) first to stop zero-click compromise.”
Microsoft is also tightening NTLM, the protocol whose hashes the Outlook bug exposes. The Windows 11 security update KB5132061 enables clients to offer NTLM message signing by default for non-anonymous connections, a change the company said “helps reduce exposure to NTLM relay attacks.”
Childs doesn’t expect the counts to fall back. “Logging back-to-back months above 1,000 CVEs proves automated bug-hunting has permanently reset patch volume,” he told The Register. “With AI making patch-diffing and exploit generation near-instant, the threat window opens the minute these updates drop.” Tuesday’s release took Microsoft past 5,160 disclosed vulnerabilities this year, Narang noted in comments reported by The Record, with the December update still to come on Dec. 8.


 WebProNews is an iEntry Publication